Keystore node A
One service-held share
A stays hereHuman verification for critical actions
Verify the person. Keep them involved in the approval. Connect BioTone’s multimodal checks and distributed signing design to the systems you already use.
Your biometrics. Your participation. Your control.
In BioTone’s three-of-three design, the two service-held shares cannot authorize a signature without the personal third share.
One service-held share
A stays hereYour personal third share
U stays with youPersonal participation includedA second service-held share
B stays herePartial signatures combine. The long-term key does not.
Shares cooperate without reconstructing the complete long-term signing key. Your application validates the result and decides whether the requested action may proceed.
Signing-key custody and biometric-data storage are different boundaries. Temporary decryption keys and templates can be used in memory. Device integrity, policy, and authorized recovery remain part of the design.
Explore the security architecture →Start with the action you need to protect
Verify the person behind mission access.
Explore the workflow →
Put a verified person behind the approval.
Explore the workflow →
Verify access around the people delivering care.
Explore the workflow →
Make sensitive operations a deliberate decision.
Explore the workflow →Illustrative industry scenes, generated for this concept. No customer or agency endorsement implied.
Planning a physical capture point? Explore hardware options →
Multimodal verification
Combine selected identity matchers with presentation or pulse checks. Matching and liveness answer different questions.
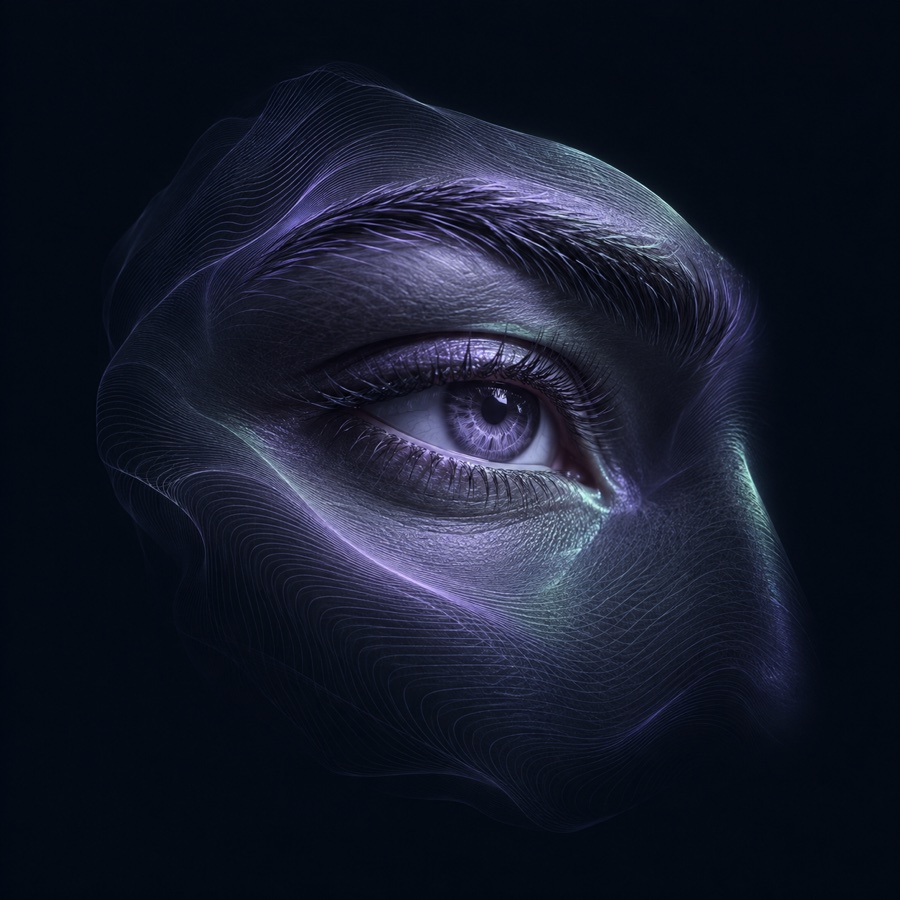
Features around the eye. Distinct from experimental iris recognition.
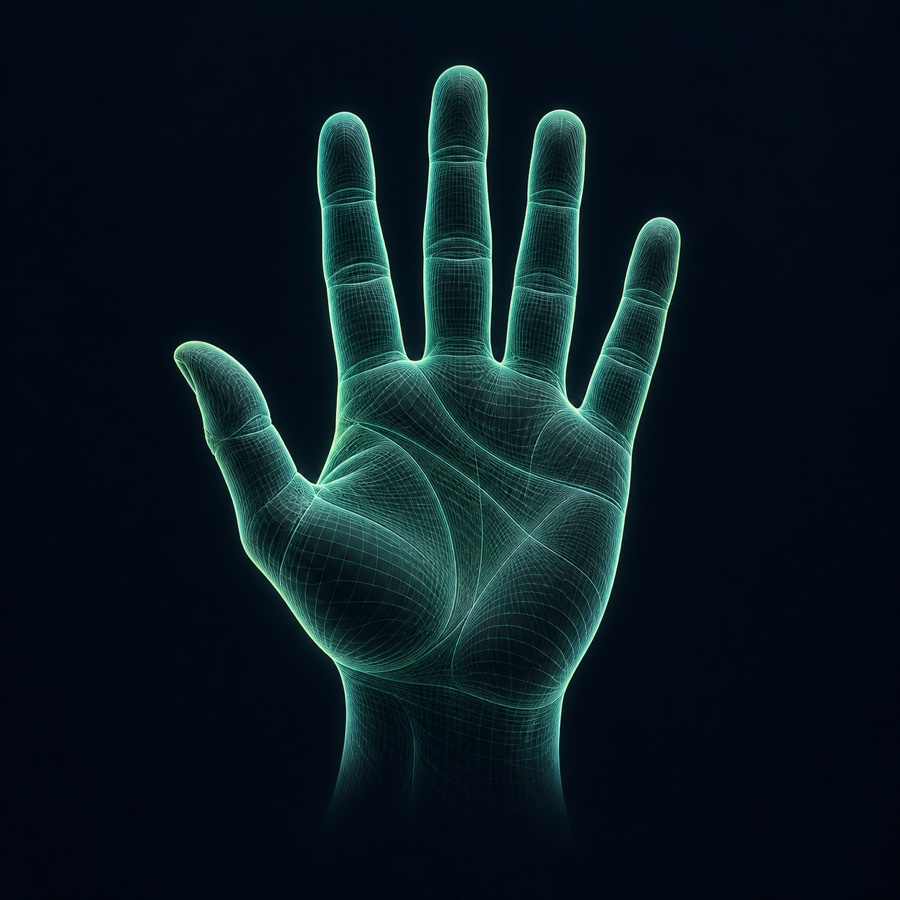
The texture and line structure of a contactless palm capture.
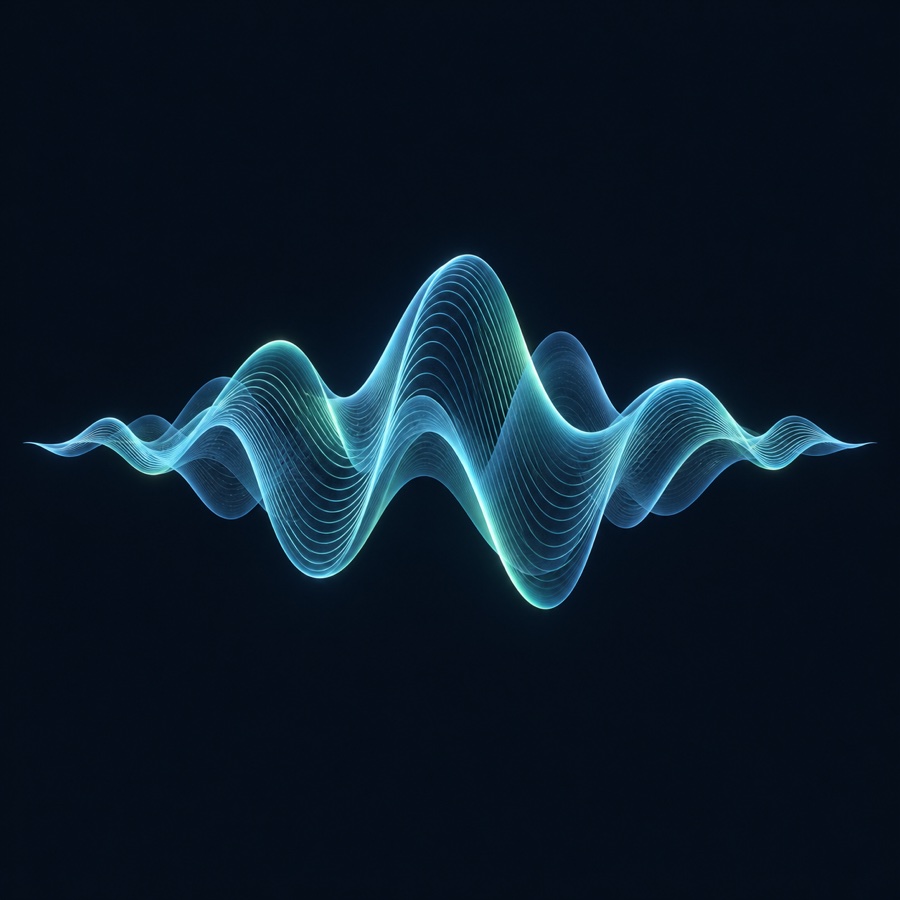
Speaker characteristics, paired with a spoken challenge.
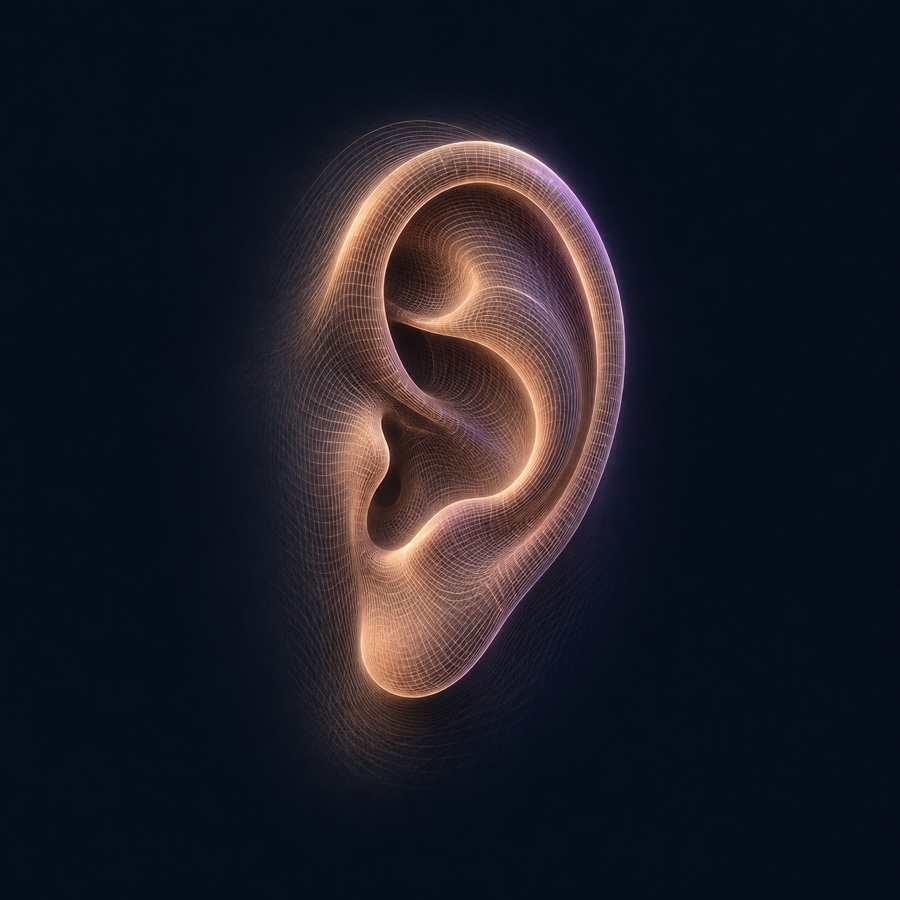
Structure captured from a side-view image.
Concept illustrations. Current mobile matchers shown; availability depends on build, device, and policy.
Explore signals and liveness checks →Verification effort & policy
Different actions call for different evidence. Explore the wallet roadmap from a brief appearance check to the full ceremony.
Concept illustrationExperimental
A front-camera burst uses face or periocular evidence. It explores a lighter interaction for routine re-checks.
Explore returning to an already-open app.
The fast path does not unlock the wallet or complete a sign-in. Camera-specific presentation-attack performance still needs validation.
Adaptive selection · experimental
The wallet prototype chooses a next challenge using the action’s requirement, enrolled signals, presentation-check results, and paths already tried.
This is a qualitative roadmap, not an accuracy scale or measured speed comparison. Face and periocular share an appearance channel; pulse and lip-sync are not additional identity factors. Continuous-session work is experimental and does not establish continuous human presence. Experimental paths do not replace the current sign-in ceremony.
Plan the right verification flow for your pilot →Connect to the systems you use
Choose the processing path that fits your product and deployment requirements.
Illustrative processing flow · storage, custody, and recovery depend on the integration.
Phone boundary
Guided capture
Capture and matching share a device.
Your application boundary
Validate the result
Check permission
Record the decision
Your system controls the action.
This mobile-broker pattern hands a verification result to your backend. Review enrollment storage, key custody, and any optional uploads for the selected build.
Where the enrollment reference is stored, how the backend validates a result, and whether this build enables any uploads.
See the workflow
Connect an enrolled person to a specific request, then apply your access policy.
Your application starts a verification flow for the requested file.
The required checks complete and your backend validates the result.
The account has permission for this file. Your application allows access and records the decision.
This result applies to the requested file. Other resources still require their own permission checks.
The people behind BioTone
Roger W. Ach II and Benjamin Portman lead BioTone, with advisors bringing experience across cybersecurity, government, identity, science, and enterprise leadership.
Meet the leadership and advisors →Turn one workflow into a measurable pilot
Bring one requirement, an integration owner, and the devices people will use. Agree on the verification, custody, recovery, and acceptance criteria together.