Enroll on device
Users complete guided capture for the signals enabled in their deployment. Agree consent, storage, and deletion requirements before enrollment.
Periocular, palm, voice, and ear matching provide identity evidence. Pulse and presentation checks add evidence of live participation. Your policy selects the required combination; supported checks depend on the device and integration. Iris recognition is experimental.
Enroll a person, verify a request, and connect the result to your access system.
Users complete guided capture for the signals enabled in their deployment. Agree consent, storage, and deletion requirements before enrollment.
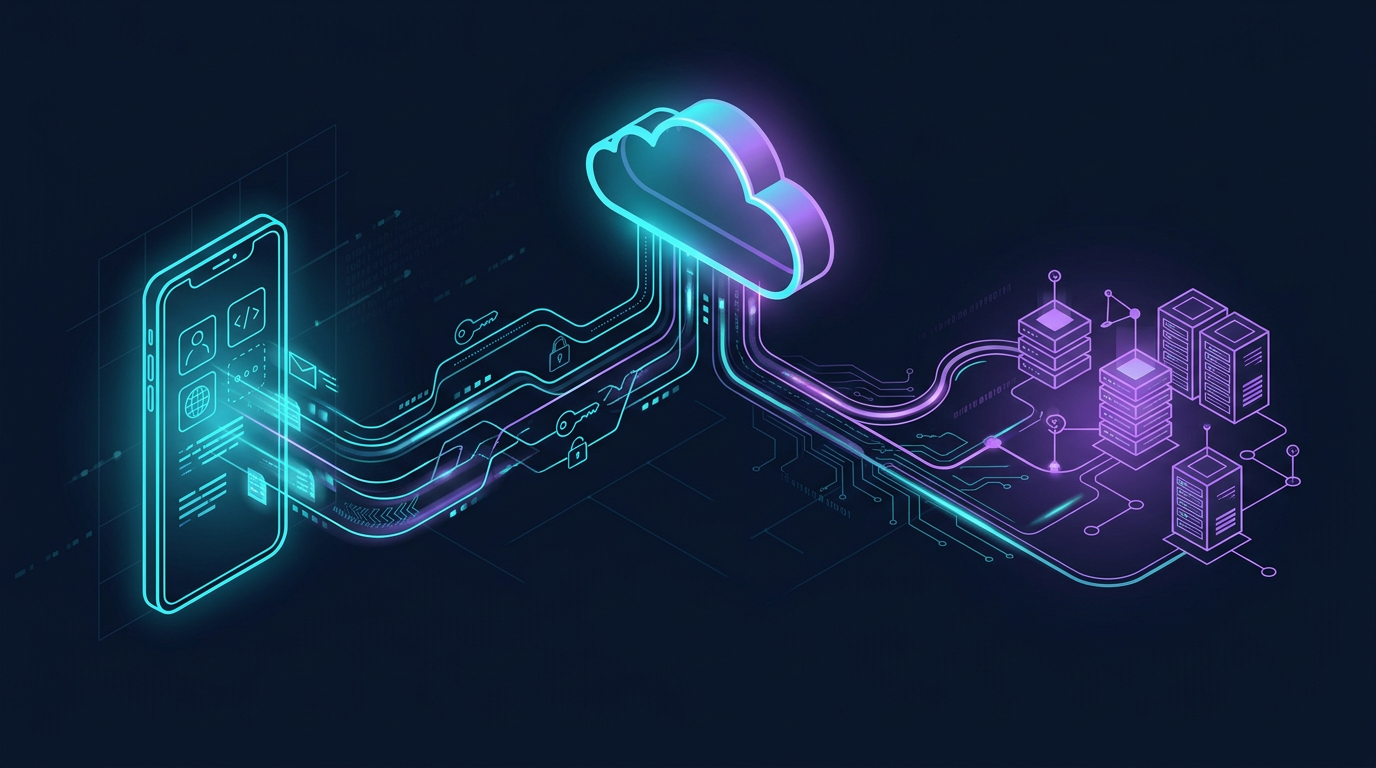
A session applies the configured matching and liveness rules. Processing location depends on the mobile, API, or Edge integration you choose.
Connect verification results to your identity provider or application backend. Validate the selected integration and its access policies in your pilot.
Experimental tiered verification explores quick checks for lower-risk moments and additional checks before sensitive actions. Evaluate interruption, reliability, and accessible fallback before enabling a repeated-verification workflow.
Define when a fresh check is needed, how users consent, and what happens if a check fails.
Let someone verify on their enrolled phone while using a browser or kiosk. A QR code or deep link opens the request; your backend validates the returned result before allowing the action.
Start with hosted services, or discuss customer-operated components and self-hosting requirements. Confirm which deployment options are ready for your pilot, including connectivity and key custody.
Bring one workflow and your identity-provider requirements. We will map the capture, verification, and access decision together.